The water utility cyberattack wave of summer 2026 used no clever exploit. According to the FBI and CISA, attackers reached controllers that answered from the open internet and changed their passwords and network addresses. Operators lost the ability to see and run parts of their own plants.
It started in Minnesota and spread to utilities in other states. For anyone who runs a municipal water, wastewater or pumping system in Ontario, the details matter, because the same equipment and the same shortcuts exist here.
This post covers why the water utility cyberattack happened, when, how the attackers worked, and the steps that would have stopped it.
When the Water Utility Cyberattack Wave Began
According to Minnesota IT Services, as reported by SecurityWeek, a coordinated attack hit the operational technology of more than 30 community water systems on July 26 and 27, 2026. Cities including Maple Plain, Braham, South St. Paul and Plymouth reported disruptions to automated control functions.
A federal warning about the water utility cyberattack came on July 30, 2026, when the FBI and the Environmental Protection Agency published public service announcement I-073026-PSA. It says that since July 27, water and wastewater utilities in at least seven states had reported incidents to the FBI, and that some of that activity degraded water operations.
The same day, CISA issued an alert to the water and wastewater sector. It reported “a significant increase” in threat actors targeting programmable logic controllers (PLCs) and urged owners, operators and integrators to take exposed PLCs off the internet as soon as possible.
Why It Happened: Controllers Anyone Could Reach
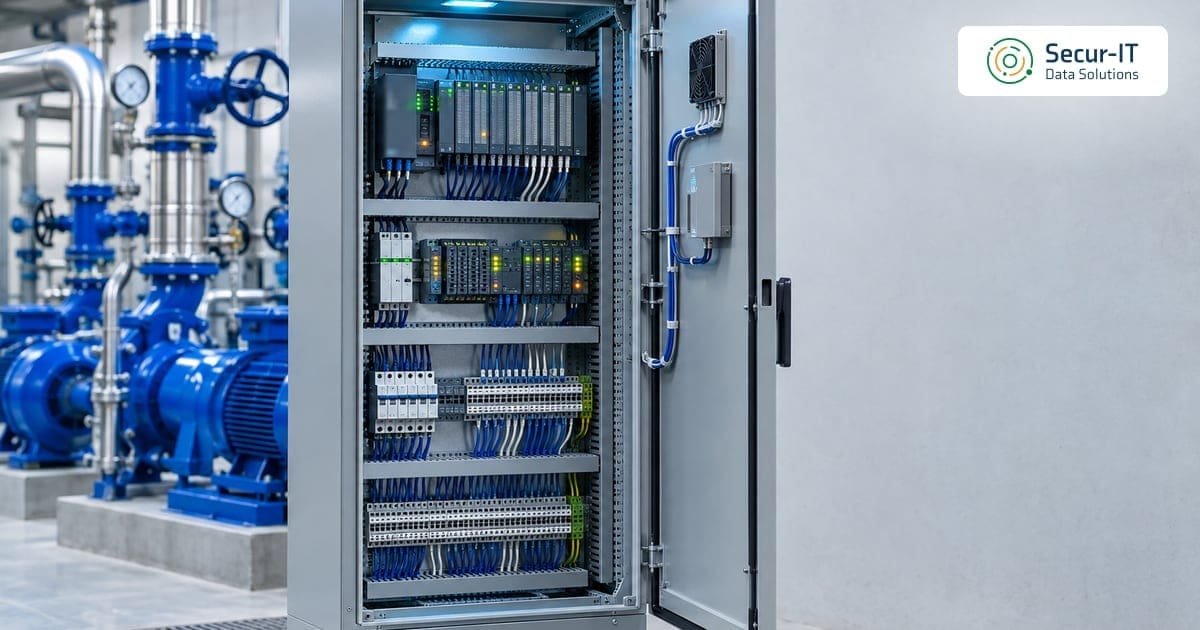
A PLC is a small industrial computer that controls pumps, valves, pressure and temperature. The Canadian Centre for Cyber Security explains in its advisory on the global PLC campaign that attackers use internet scanning services to find exposed PLCs, then take advantage of weak, default or absent passwords.
The same advisory says many PLCs are exposed by accident, without the owner knowing. Three conditions came up again and again in the government guidance:
- Forgotten connections: CISA warned that the targeting includes cellular modems installed by operators, vendors or system integrators that may not be documented or caught by routine scans. The Canadian Centre for Cyber Security adds that these links are often kept after they are no longer needed.
- Shared setups: the FBI and EPA announcement notes that similar network setups provided by third parties across several victims may have let the attackers repeat their success from one customer to the next.
- Old hardware: the same announcement warns that end-of-life devices no longer receive security updates and are routinely targeted.
None of these is a sophisticated flaw. A water utility cyberattack of this kind succeeds because a controller that should only talk to the plant network also talks to the world.
How the Attackers Worked
The FBI and EPA announcement names the equipment: Rockwell Automation/Allen-Bradley MicroLogix 1100 and 1400 series PLCs. It adds that operators of other PLC brands should take the same precautions.
The method behind each water utility cyberattack, as the announcement describes it, was simple:
- Remote access: the actors reached PLCs that faced the internet directly.
- Lockout: they changed IP addresses and turned on or changed passwords, so operators lost monitoring and control.
- Logic changes: at least one organization found modified PLC project files after it noticed ladder logic discrepancies across several sites.
The effects depended on what each controller did and whether staff could switch to manual operation. The FBI said effects reported to it included loss of pressure and flooding, and warned that pressure loss could let untreated groundwater seep into pipes.
What Each Source Said About Water Safety and Attribution
The public record on this water utility cyberattack does not agree on every point, so it is worth being exact.
On water safety, the affected Minnesota cities told residents that their drinking water remained safe, as SecurityWeek and Industrial Cyber both reported. CISA’s alert, written for the whole campaign rather than one state, said the activity “resulted in boil water notices and sustained manual operations” but did not name the utilities involved.
On attribution, SecurityWeek reported that state and federal agencies were still investigating and that no formal attribution had been made. Some news reports pointed to Iran-linked groups. We found no government statement that confirms that link for these incidents, so we do not make it here.
The Canadian Picture
This is not only an American story. The Canadian Centre for Cyber Security says it observed several incidents affecting industrial control systems in Canada in October 2025, and in one of them a threat actor manipulated water pressure valve controls at a municipal water system, causing minor impacts to water service.
The same advisory says Canada has not had a high-impact industrial control system incident so far. It also assesses that the threat is increasing and that future incidents will likely be more severe. A water utility cyberattack like the Minnesota wave is the kind of event that guidance is written to prevent.
We covered the earlier Canadian hacktivist alert in our post on exposed ICS devices in Canada. The lessons below build on it with what the 2026 campaign added.
How to Avoid a Water Utility Cyberattack at Your Plant
Each step below comes from a government source named in the same item. None of them requires new process control equipment.
- Take PLCs off the internet: CISA’s alert says to disconnect the PLC from the internet and route any remote access through a VPN or gateway, never straight to the controller.
- Scan your own address ranges: the Canadian Centre for Cyber Security tells organizations to scan the internet address ranges they own, and to check connections set up by third parties that nobody manages anymore.
- Find every cellular modem: walk the remote sites, lift stations and reservoirs. The FBI and EPA announcement says modems should have strong authentication, current updates and logs that someone reviews.
- Change default passwords: CISA’s primary mitigations for operational technology says to change default passwords immediately and use strong, unique ones.
- Use MFA on remote access: the same CISA guidance calls for a VPN with a strong password and phishing-resistant multifactor authentication, and for disabling dormant accounts. The Canadian Centre for Cyber Security’s ICS security guidance also recommends individual accounts with MFA.
- Allow only expected traffic: CISA recommends allowlisting so remote access comes only from known engineering laptops, and the FBI suggests access control lists on the PLC itself.
- Keep the key in RUN: the FBI and EPA announcement says to keep physical and software key switches in the run position, and to move them only while you update the program.
- Back up project files and ladder logic: CISA says to keep a known clean backup of the PLC image in case a changed password locks you out. The FBI adds that you should check a backup for malicious logic before you restore it.
- Drill manual operation: the FBI and EPA announcement and CISA’s mitigations both say to practice running the plant by hand and to test those plans routinely.
- Watch OT traffic and logs: the Canadian Centre for Cyber Security recommends logging and monitoring all access and events, so a password change in the middle of the night raises an alarm.
Who Owns the Integrator Connection
Many small water systems rely on an integrator or service provider who set up remote access years ago. The Canadian Centre for Cyber Security says the risk of unknown exposure is greatest for these organizations, and that an unclear split of roles often leaves critical systems unprotected.
Its advice is practical. Work with your integrators so systems stay secure for their whole life, and consider writing maintenance, security duties and liability into the service agreement.
Ask three plain questions this month. Which of your controllers can your integrator reach today? How does that connection log in?
Then ask who turns it off when the work is done. Write the answers down and keep them with your emergency response plan.
Where Secur-IT Data Fits
Our OT security services focus on the networks around SCADA, PLCs, HMIs and other OT assets, and our team works alongside your plant and engineering staff. For a water or wastewater operator, that maps closely to the steps above:
- OT asset and traffic discovery: finding every device on the OT network and mapping network zones, data flows, remote access and vendor connectivity.
- Network segmentation and remote access hardening: separating control systems from IT and the internet, and tightening vendor and engineer connections.
- OT monitoring: monitoring use cases built for OT, with high-level playbooks for escalation and containment.
- One-way data flows: data diodes that let plant data reach reporting or a SIEM without opening a path back into the control network.
Most operators start with our OT security starter engagement: an asset and flow visibility assessment, the identification of one high-risk data flow, and a high-level design to protect it. It is quoted after a short scoping call. A water utility cyberattack is far easier to prevent with that map in hand.
Frequently Asked Questions
Q: What happened in the 2026 water utility cyberattack wave?
Starting July 26, 2026, attackers reached internet-exposed PLCs at water and wastewater utilities, changed their passwords and IP addresses, and locked operators out of monitoring and control. Minnesota reported more than 30 affected community water systems, and the FBI said utilities in at least seven states reported incidents.
Q: Which equipment was targeted?
The FBI and EPA named Rockwell Automation/Allen-Bradley MicroLogix 1100 and 1400 series PLCs. They added that owners of other PLC brands should take the same precautions.
Q: Was drinking water affected?
The affected Minnesota cities told residents their drinking water remained safe. CISA’s alert for the wider campaign said the activity resulted in boil water notices and sustained manual operations, without naming the utilities.
Q: Has a water utility cyberattack happened in Canada?
The Canadian Centre for Cyber Security reports that in October 2025 a threat actor manipulated water pressure valve controls at a Canadian municipal water system, with minor impacts. It says Canada has not had a high-impact industrial control system incident so far.
Q: What is the first step for a small Ontario water system?
Find out which of your controllers, HMIs and cellular modems answer from the internet. Scan the address ranges you own, ask your integrator about every remote connection, and remove direct exposure first.
References
- FBI and EPA: Public Service Announcement I-073026-PSA, Malicious Cyber Actors Targeting Water and Wastewater Sector Internet-Facing PLCs
- CISA: CISA Urges Water and Wastewater Systems Sector to Protect OT Against Activity Targeting PLCs
- Canadian Centre for Cyber Security: Cyber threat actors use artificial intelligence in an active global campaign to disrupt internet-exposed programmable logic controllers
- CISA, FBI, EPA and DOE: Primary Mitigations to Reduce Cyber Threats to Operational Technology
- SecurityWeek: CISA Urges Water Sector to Protect OT After Coordinated Attacks on PLCs
Ready to Strengthen Your Cybersecurity?
Secur-IT Data Solutions is a Toronto-based MSSP providing enterprise-grade cybersecurity for Canadian businesses. Whether you need OT security, AI threat protection, penetration testing, or full managed security services, our team is ready to help.
Talk to our team:
- 📞 Call us: +1 (647) 948-6768
- 📧 Email: info@securitdata.ca
- 🌐 Book a scoping call →
Krikor Tengerian is the CEO and founder of Secur-IT Data Solutions, a Toronto-based cybersecurity firm focused on helping Canadian organizations secure their infrastructure and critical systems. With over 25 years of experience across cybersecurity and IT infrastructure, he has supported organizations in hardening networks, protecting critical workloads, and aligning security controls with business and regulatory requirements.
Krikor actively shapes the direction and themes of Secur-IT’s educational content, collaborating with AI tools to structure, refine, and expand articles while providing the real-world context, use cases, and review to keep them accurate and practical for readers. He regularly shares insights on OT security, threat detection, incident response, and Canadian cybersecurity compliance to help industrial and commercial organizations better understand and reduce their cyber risk.